Microsoft patents system that maps network roles to find security gaps
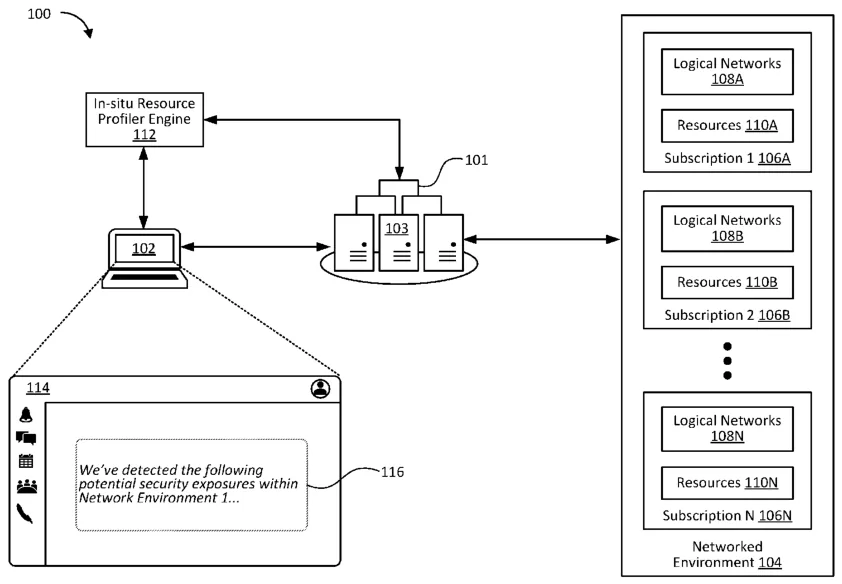
Microsoft describes a software engine that maps out the different levels of a computer network to understand how each part fits into the overall structure. It creates detailed profiles for each component based on its specific role and how it interacts with others. By analyzing these profiles, the system can identify potential security weaknesses within the network.
In the filing’s own words
Systems and methods herein provide an in-situ resource profiler (IRP) engine and its related functions. In an aspect, an IRP engine may identify a plurality of hierarchy levels within a networked environment, wherein the plurality of hierarchy levels defines an organizational architecture of a plurality of resources. The IRP engine may determine hierarchy-level context of each hierarchy level and generate a plurality of resource profiles for the plurality of resources based on the hierarchy-level context. The resource profiles may include a resource role and design pattern of a respective resource within the networked environment. Based on the plurality of resource profiles, the IRP engine may detect one or more potential security exposures within the networked environment.
What exactly they claim (claim 1)
1. A computing apparatus comprising: a computer-readable storage media comprising processor-executable instructions stored thereon; and a processor coupled to the computer-readable storage media and configured to execute the processor-executable instructions that, when executed by the processor, direct the computing apparatus to at least: access a contextual security representation of a networked environment, wherein the contextual security representation comprises a plurality of resources; identify a plurality of hierarchy levels associated with the plurality of resources within the contextual security representation; determine a plurality of hierarchy-level context for the plurality of hierarchy levels, wherein individual hierarchy-level contexts within the plurality of hierarchy-level context correspond to respective hierarchy levels within the plurality of hierarchy levels; generate a plurality of resource profiles for the plurality of resources based on the hierarchy-level context, wherein a resource profile of the plurality of resource profiles corresponds to a respective resource of the plurality of resources; and publish the plurality of resource profiles for the plurality of resources within the contextual security representation.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- IN-SITU RESOURCE PROFILER ENGINES FOR DETECTING SECURITY EXPOSURES WITHIN A NETWORKED ENVIRONMENT
- Publication number
- US20260361749A1
- Application number
- 19202216
- Filed
- May 8, 2025
- Published
- Nov 12, 2026
- Inventors
- 1
- Claims
- 20
Classified under
H04L 63/1433 Electricity & electronicsH04L 63/205 Electricity & electronicsMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents video verification to confirm real people in clips Nov 10, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.