Microsoft patents system using multiple AI models to spot fake login attempts
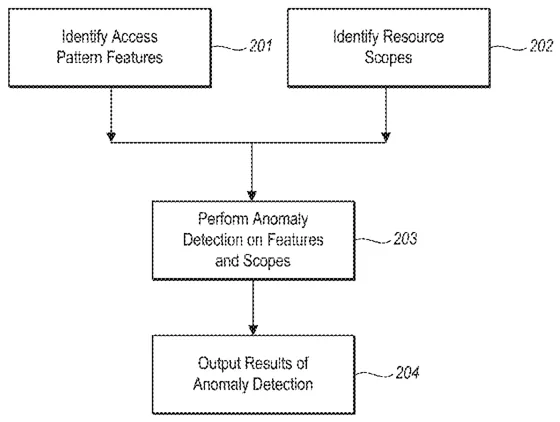
Microsoft describes a security system that checks if a request to access a file or service is suspicious by looking at many different details at once. Instead of using one single check, it splits the data into groups and assigns a specific machine learning model to each group to analyze it. This approach helps the system detect unusual activity even when the user or the server is using virtual locations that hide their true physical position.
In the filing’s own words
Multiple variate anomaly detection against multiple scopes of the requested resource. Even if one of the variates patterns is sensitive to physical location of the requestor and/or the resource, not all of the variates of the access pattern will be. Furthermore, even if one of the scopes of the resource is sensitive to physical location of the resource, not all scopes will be. Thus, the use of multiple variates of the access pattern and multiple scopes of the anomaly detection allows for better estimates of anomaly detection to be made, even when the source of the access request is virtualized and/or the location of the resource is virtualized.
What exactly they claim (claim 1)
1. A computer system comprising: one or more hardware processors; and one or more hardware storage devices that store instructions that are executable by the one or more hardware processors to cause the computer system to: access a request for a resource; identify a plurality of features associated with the request; identify a plurality of scopes of the resource; form a set of combinations by associating each one of the features with each one of the scopes such that said each feature is included in multiple different combinations, with each one of those different combinations having a different scope; form combination groupings by grouping the different combinations in the set using each of the features as a basis; for each one of the combination groupings, dedicate a corresponding machine learning model to said each one combination group such that multiple machine learning models are dedicated, wherein each respective multiple machine learning model is tasked with performing anomaly detection for its respective combination grouping; cause the multiple machine learning models to perform anomaly detection on their respective combination groupings; and output one or more results from the multiple machine learning models.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- Multi-variate anomalous access detection
- Patent number
- US12804000B2
- Application number
- 18792870
- Filed
- Aug 2, 2024
- Granted
- Nov 17, 2026
- Inventors
- 2
- Claims
- 20
Classified under
H04L 63/1425 Electricity & electronicsG06F 18/2178 Physics & computingG06N 20/00 Physics & computingH04L 63/0236 Electricity & electronicsH04L 63/104 Electricity & electronicsH04L 63/1416 Electricity & electronicsMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents video verification to confirm real people in clips Nov 10, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.