Microsoft patents secure error handling for cloud connections to local servers
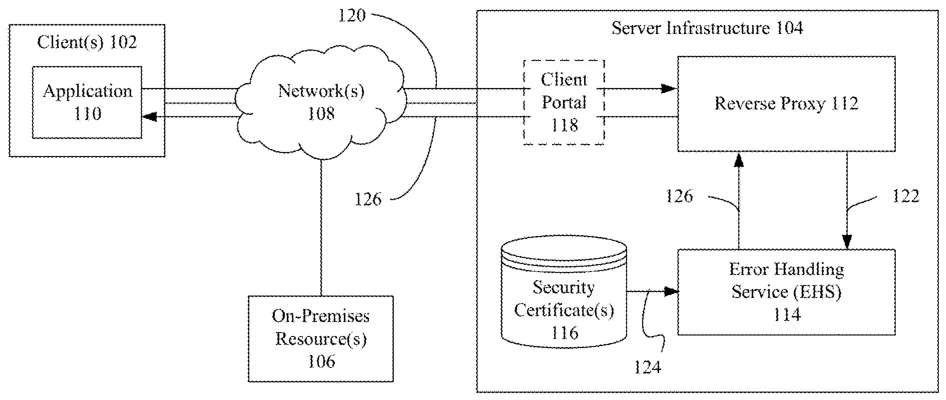
This patent describes a method for handling errors when a cloud service tries to connect to a private server on a company's local network. If the connection fails, a reverse proxy sends details to a separate error handling service, which then sends a secure, encrypted error message back to the user through the existing connection.
In the filing’s own words
System, methods, apparatuses, and computer program products are disclosed for injecting custom information for a server while establishing end-to-end secure communications with a client via a tunneling service. A reverse proxy receives, from a client over a first transport-layer connection, a request that includes an identifier associated with an on-premises resource. The reverse proxy determines, based on the identifier, that an error prevents forwarding of the client request to the on-premises resource. In response, the reverse proxy transmits, to an error handling service (EHS) over a second transport-layer connection, a new application-layer request comprising error handling information to enable the EHS to establish, via the reverse proxy, a secure communications channel with the client using the existing first transport-layer connection and the second transport-layer connection. The reverse proxy proxies, from the EHS and to the client, an encrypted response containing an error message.
What exactly they claim (claim 1)
1. A method for error handling while establishing end-to-end encrypted communications with a client, the method comprising: receiving, at a reverse proxy of a cloud service over a first transport layer connection, a client request that includes a resource identifier associated with an on-premises resource, the reverse proxy lacking access to security information associated with the on-premises resource; determining, based at least on the resource identifier, that an error prevents forwarding of the client request to the on-premises resource; transmitting, to an error handling service over a second transport layer connection, an application layer request comprising error handling information, the error handling service configured to access the security information associated with the on-premises resource and establish a secure communications channel with the client over the second transport layer connection and the first transport layer connection; receiving, from the error handling service, an encrypted response comprising an error message generated based at least on the error handling information, the encrypted response encrypted with security information associated with the on-premises resource; and forwarding, to the client, the encrypted response.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- Custom information injection for a server while establishing end-to-end secure communication with a client via tunneling service
- Patent number
- US12803968B2
- Application number
- 18530777
- Filed
- Dec 6, 2023
- Granted
- Nov 17, 2026
- Inventors
- 6
- Claims
- 20
Classified under
H04L 63/0823 Electricity & electronicsH04L 41/0631 Electricity & electronicsH04L 63/0435 Electricity & electronicsH04L 67/2895 Electricity & electronicsMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents video verification to confirm real people in clips Nov 10, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.