Microsoft patents method to check code-checking tools against real execution
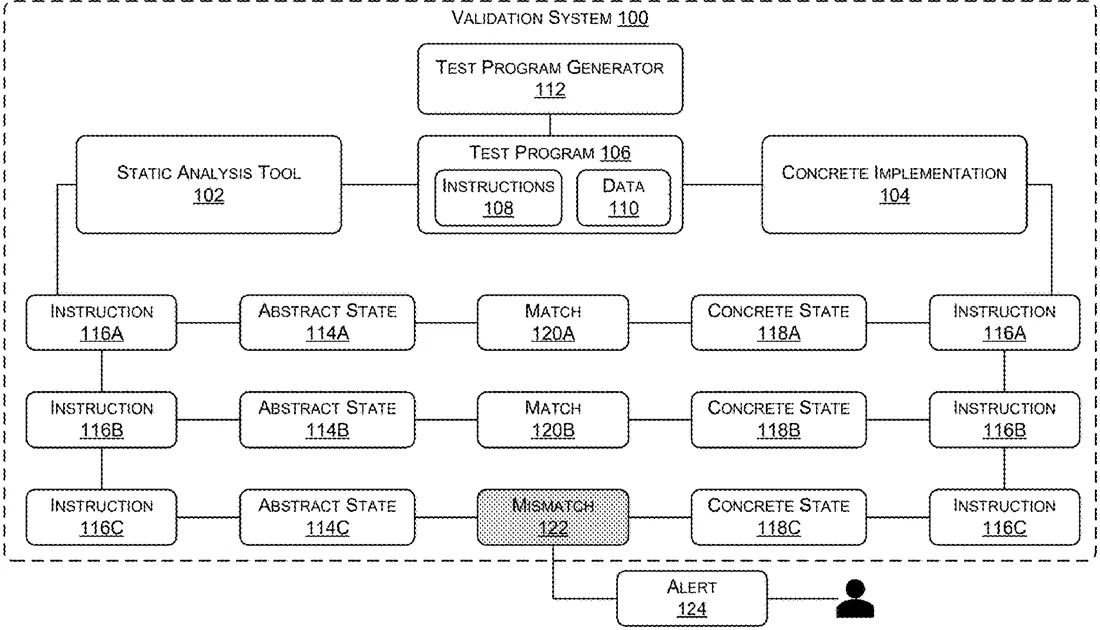
Microsoft describes a system that verifies static analysis tools by comparing their predicted code behavior against actual execution results. The method runs a test program in both a mathematical model and a real environment, flagging any differences between the expected and actual outcomes. This helps developers find bugs in the analysis tool itself rather than just the code it is checking.
In the filing’s own words
The techniques presented herein provide a system for validating a static analysis tool by utilizing a comparison between an abstract state computed by the static analysis tool and a concrete state output by a concrete implementation. A static analysis tool is an automated software tool that evaluates the behavior of a given computer program using rigorous mathematical methods and without executing the program. In contrast, a concrete implementation is an actual machine (e.g., a virtual machine) that executes the given computer program to observe the behavior of the computer program under real world circumstances. Detecting a mismatch between the abstract state and the concrete state is a definite indication of at least one issue (e.g., a bug). As such, utilizing both the abstract state and the concrete state to validate the static analysis tool streamlines the process of discovery, diagnosing, and addressing issues.
What exactly they claim (claim 1)
1. A method for validating a static analysis tool comprising: receiving a test program comprising a sequence of instructions and data for initializing the test program; computing, by the static analysis tool, an abstract state of the test program for an instruction of the sequence of instructions, wherein the abstract state defines an expected value for the instruction that is identified as valid by the static analysis tool; generating, by a concrete implementation executing the test program, a concrete state of the test program for the instruction of the sequence of instructions, wherein the concrete state includes a specific value that is calculated from an execution of the instruction using the data; identifying a mismatch between the concrete state and the abstract state at the instruction of the test program, wherein the mismatch is identified by the by specific value included in the concrete state being different from the expected value defined by the abstract state; and in response to identifying the mismatch, generating an alert, wherein the alert identifies the instruction that caused the mismatch between the concrete state and the abstract state.
Facts
- Company
- Microsoft (MICROSOFT TECHNOLOGY LICENSING, LLC)
- Official title
- VALIDATION OF STATIC ANALYSIS TOOLS VIA COMPARISON OF CONCRETE AND ABSTRACT STATES
- Publication number
- US20260300142A1
- Application number
- 19089395
- Filed
- Mar 25, 2025
- Published
- Oct 1, 2026
- Inventors
- 2
- Claims
- 20
Classified under
G06F 11/3684 Physics & computingG06F 11/3692 Physics & computingMore from Microsoft in AI & software
- Microsoft patents method to check AI answers against verified facts Oct 20, 2026
- Microsoft patents AI that presents PowerPoint slides for you Sep 3, 2026
- Microsoft patents method to check if LLM answers are based on real data Sep 10, 2026
- Microsoft patents system to blend multiple AI agents into one chat Oct 1, 2026
- Microsoft patents system that answers questions using your screen history Oct 15, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.