Microsoft patents AI system that combines threat and anomaly checks for security
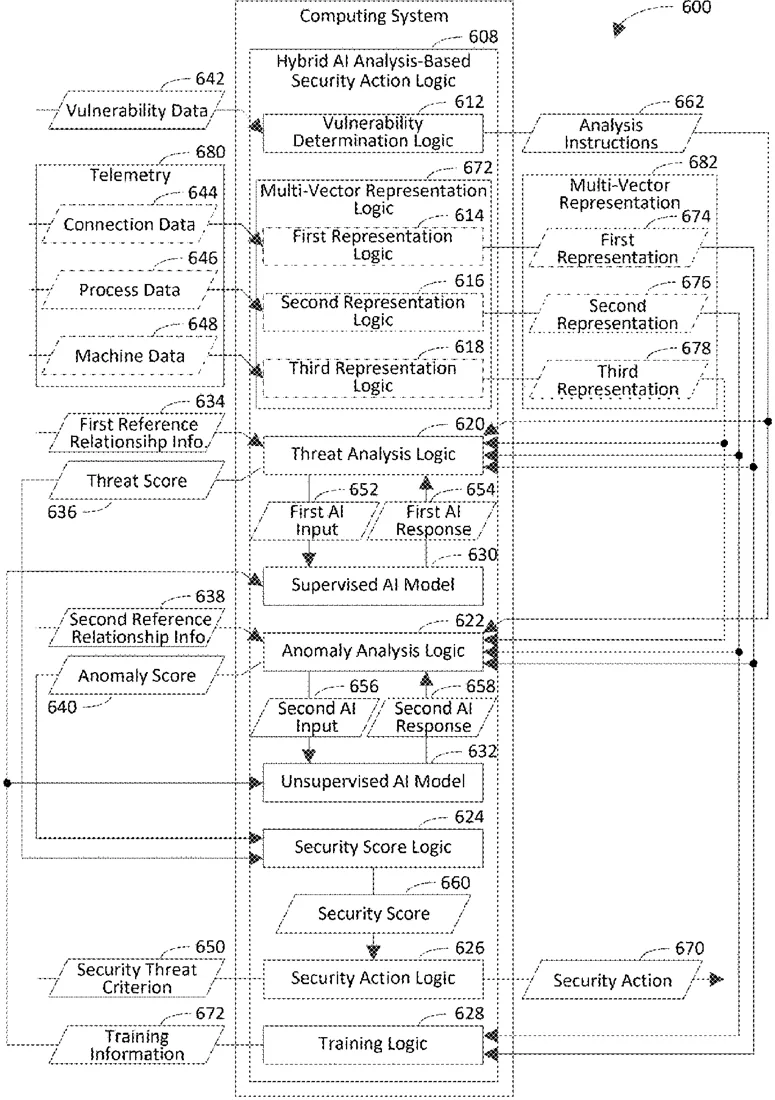
Microsoft has filed a patent for a security system that uses two different AI models to monitor computer activity. One model checks if the activity matches known attacks, while the other looks for unusual behavior that doesn't fit the machine's normal pattern. The system combines these two checks into a single score to decide if a security action is needed.
In the filing’s own words
Techniques are described herein that are capable of performing a multi-vector correlation using threat and anomaly analyses to assess a real-time security threat. A supervised AI model is caused to determine a first extent to which relationships between more than two vectors in a multi-vector representation, which indicate telemetry associated with a machine, correspond to first reference relationships associated with a known security threat. An unsupervised AI model is caused to determine a second extent to which the relationships differ from second reference relationships associated with a machine type of the machine. A security score is generated by combining indications of the first and second extents. A security action is performed as a result of the security score satisfying a security threat criterion.
What exactly they claim (claim 1)
1. A system comprising: a processor system; and a memory that stores computer-executable instructions that are executable by the processor system to at least: generate a multi-vector representation that indicates telemetry associated with a machine, the multi-vector representation comprising more than two vectors; generate a threat score by analyzing relationships between the more than two vectors and first reference relationships associated with a known security threat using a supervised artificial intelligence (AI) model, the threat score indicating a first extent to which the relationships correspond to the first reference relationships; generate an anomaly score by analyzing the relationships between the more than two vectors and second reference relationships associated with a machine type of the machine using an unsupervised AI model, the anomaly score indicating a second extent to which the relationships differ from the second reference relationships; generate a security score by combining the threat score and the anomaly score; and perform a security action as a result of the security score satisfying a security threat criterion.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- MULTI-VECTOR CORRELATION USING THREAT AND ANOMALY ANALYSES TO ASSESS A REAL-TIME SECURITY THREAT
- Publication number
- US20260332619A1
- Application number
- 19185124
- Filed
- Apr 21, 2025
- Published
- Oct 22, 2026
- Inventors
- 1
- Claims
- 20
Classified under
H04L 63/1425 Electricity & electronicsH04L 41/16 Electricity & electronicsMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
- Microsoft patents security checks for AI chats using user and model profiles Oct 1, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.