Microsoft patents tool that maps apps to show security risks
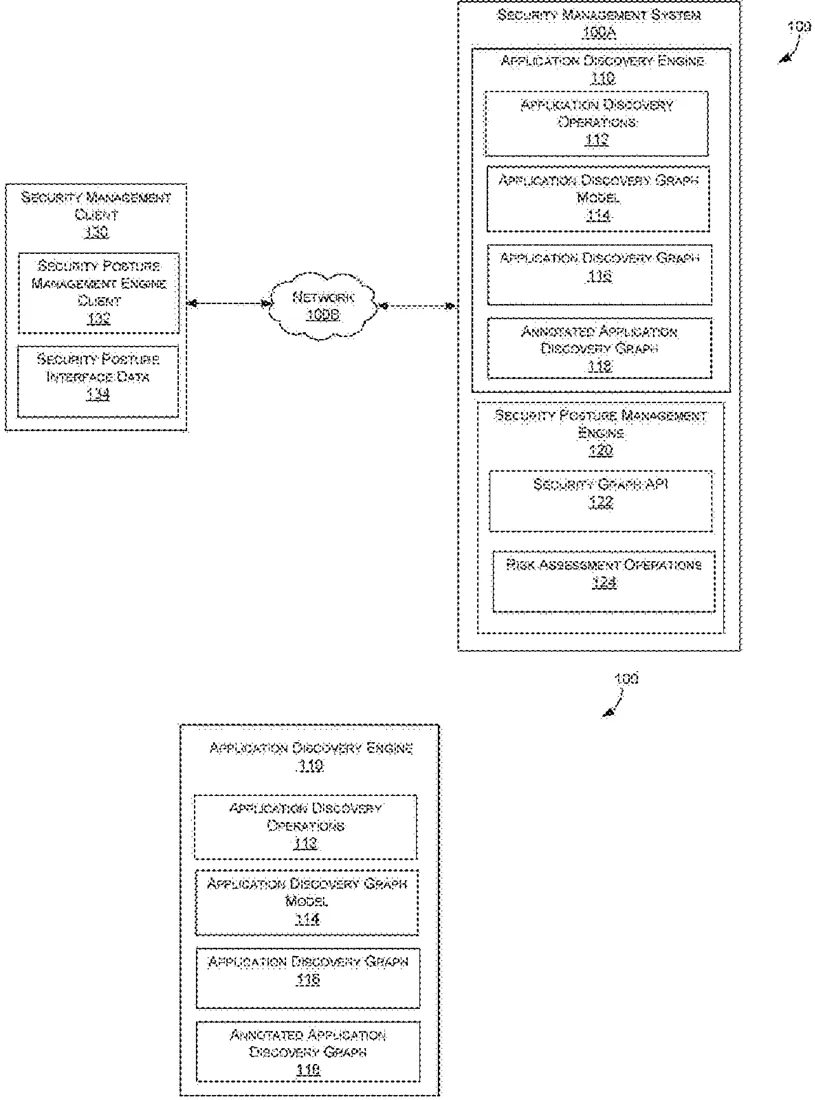
This filing describes a system that automatically finds and maps all software applications running in a company's computer network. It creates a visual diagram, or graph, of these applications and adds notes about their security status to help IT teams see where vulnerabilities exist.
In the filing’s own words
Methods, systems, and computer storage media for providing data security posture management using an application discovery engine in a security management system. Application discovery supports identifying and mapping various applications within a computing environment. In particular, application discovery can be provided as part of security management operations to assess security posture of applications, identify vulnerabilities, and ensure compliance with regulations. In operation, application discovery data associated with a plurality computing resources of a computing environment is accessed. An annotated application discovery graph comprising a plurality of entities that represent the plurality of computing resources is generated. The annotated application discovery graph is deployed to support generating security postures for computing environments. A request is received for a security posture of the computing environment. A security posture visualization that includes an application discovery graph annotation is generated. The security posture visualization is communicated to cause display of the security posture visualization.
What exactly they claim (claim 1)
1. A computerized system comprising: one or more computer processors; and computer memory storing computer-useable instructions that, when used by the one or more computer processors, cause the one or more computer processors to perform operations, the operations comprising: accessing application discovery data associated with a plurality of computing resources of a computing environment; based on the application discovery data, generating an annotated application discovery graph comprising a plurality of entities representing the plurality of computing resources, wherein generating the annotated application discovery graph comprises executing a plurality of application discovery operations that annotate the application discovery graph with one or more application discovery graph annotations based on analyzing one or more spanning trees in the application discovery graph; deploying the application discovery graph to support generating a security posture of the computing environment; receiving a request for the security posture of the computing environment; using the annotated application discovery graph, generating a security posture visualization associated with the computing environment, wherein the security posture visualization comprises an application discovery graph annotation; and communicating the security posture visualization to cause display of the security posture visualization comprising the application discovery graph annotation.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- APPLICATION DISCOVERY ENGINE IN A SECURITY MANAGEMENT SYSTEM
- Publication number
- US20260330011A1
- Application number
- 19537803
- Filed
- Feb 12, 2026
- Published
- Oct 22, 2026
- Inventors
- 4
- Claims
- 20
Classified under
G06F 21/552 Physics & computingMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
- Microsoft patents security checks for AI chats using user and model profiles Oct 1, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.