Samsung patents method to check if security data has been tampered with
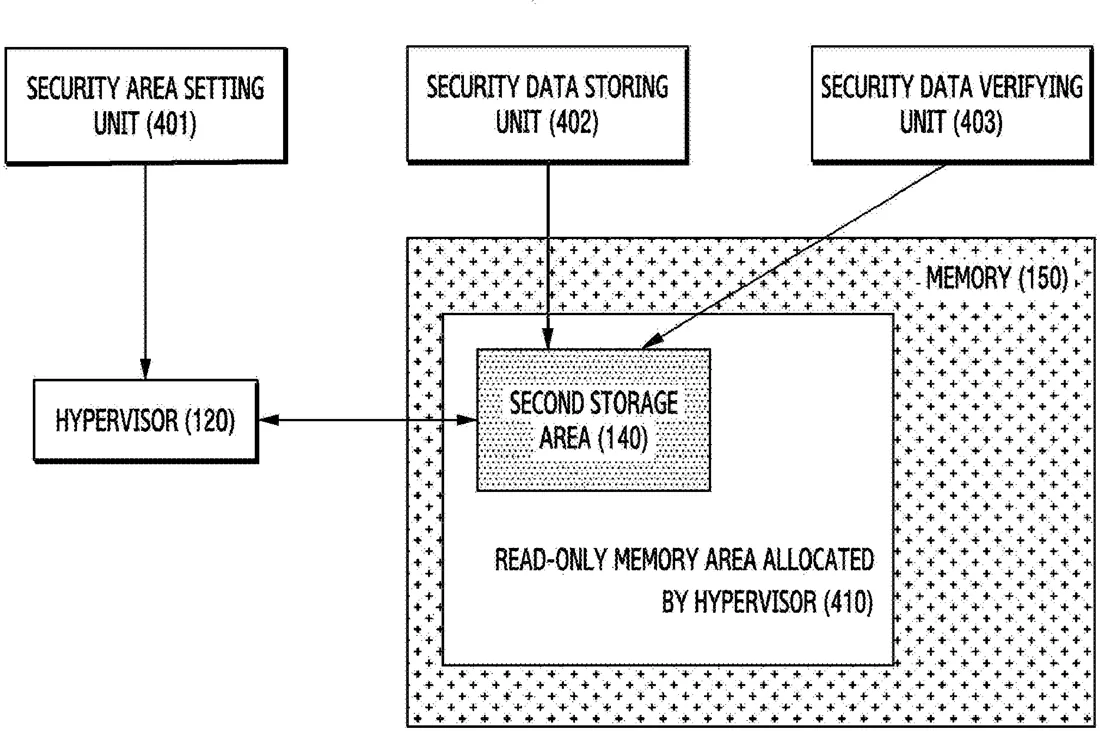
Samsung describes a system that checks the integrity of critical security data stored on a device. It works by comparing the current data against a reference copy stored in a read-only area, alerting the system if the two do not match.
In the filing’s own words
An electronic device is provided. The electronic device includes memory, including one or more storage media, storing instructions, and at least one processor, including processing circuitry, communicatively coupled to the memory, wherein the instructions, when executed by the at least one processor individually or collectively, cause the electronic device to identify an event for verification of first security data written to a first storage area, read, using the kernel, information representing an address of the first storage area to which the first security data is written and second security data, from a second storage area, and read the first security data from the first storage area using the kernel, compare the second security data and the first security data for the verification of the first security data, and based on identifying the first security data different from the second security data in accordance with comparison, provide a notification representing an abnormal state of the first security data.
What exactly they claim (claim 1)
1. An electronic device comprising: memory, comprising one or more storage media, storing instructions; and at least one processor, comprising processing circuitry, communicatively coupled to the memory, wherein the instructions, when executed by the at least one processor individually or collectively, cause the electronic device to: identify an event for verification of first security data written to a first storage area, wherein the first storage area is accessible by a kernel for reading and writing, based on the event, read, using the kernel, information representing an address of the first storage area to which the first security data is written and second security data which is reference data for verifying the first security data, from a second storage area, wherein the second storage area is accessible by the kernel for reading, and inaccessible by the kernel for writing, read, based on the address represented by the information, the first security data from the first storage area using the kernel, compare the second security data and the first security data for the verification of the first security data, and based on identifying the first security data different from the second security data in accordance with comparison, provide a notification representing an abnormal state of the first security data.
Facts
- Company
- Samsung (Samsung Electronics Co., Ltd.)
- Official title
- ELECTRONIC DEVICE, METHOD, AND NON-TRANSITORY COMPUTER READABLE STORAGE MEDIUM FOR IDENTIFYING INTEGRITY OF STORED DATA
- Publication number
- US20260330002A1
- Application number
- 19461110
- Filed
- Jan 27, 2026
- Published
- Oct 22, 2026
- Inventors
- 1
- Claims
- 20
Classified under
G06F 21/44 Physics & computingMore from Samsung in Security & privacy
- Samsung patents SSDs that use AI to spot ransomware attacks Oct 20, 2026
- Samsung patents AI system to find and fix device security flaws Sep 17, 2026
- Samsung patents method to find lost devices via nearby phones Sep 8, 2026
- Samsung patents video camera that tracks authorized faces for security Sep 1, 2026
- Samsung patents system that ranks home camera clips by unusual events Sep 8, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.