Microsoft patents security rules that add context to threat alerts
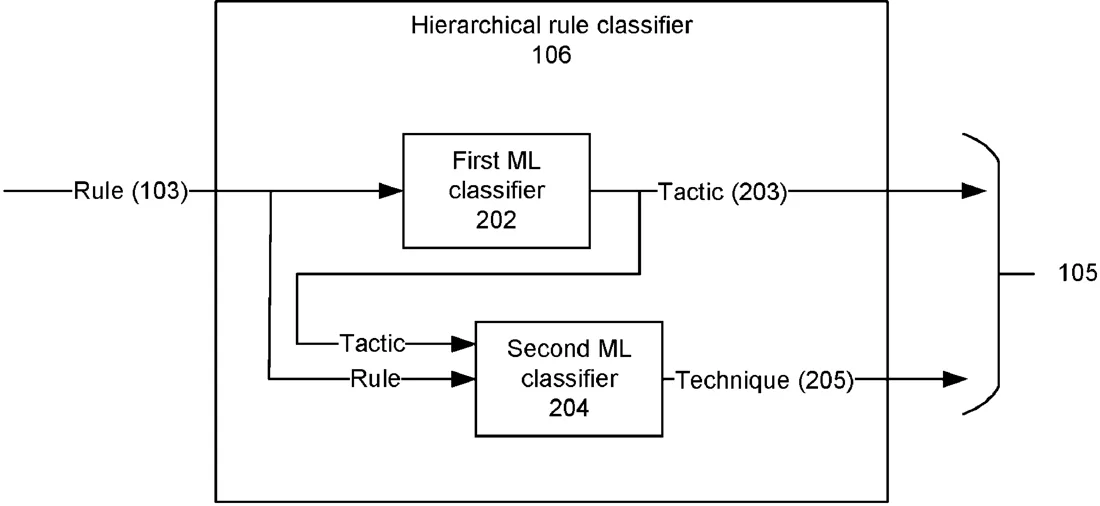
Microsoft describes a method for adding detailed context to cybersecurity detection rules using two stages of machine learning. The first stage identifies a broad threat category, while the second stage uses that result to pinpoint a specific technique. This extra information helps the system decide how to report or fix the issue when a threat is detected.
In the filing’s own words
Aspects herein pertain to a form of detection rule enrichment, in which a detection rule implemented in a security system is enriched with relevant context to assist actions such as reporting or remediation when the rule is triggered based on pattern matching to telemetry. A two-stage rule classification process is disclosed, where a first classifier assigns a first threat classification label (e.g., tactic) and a second classifier assigns a second threat classification label (e.g., technique). The classification is hierarchical in that second classifier uses the output of the first classifier (the first threat classification label) to determine the second threat classification label.
What exactly they claim (claim 1)
1. A computer-implemented method, comprising: assigning a first threat classification label to a detection rule, using a first machine learning (ML) classifier; assigning a second threat classification label to the detection rule, using a second ML classifier based on the first threat classification label; causing a cybersecurity detector to implement the detection rule on collected telemetry; and causing a response engine to implement, in response to an activation of the detection rule, a threat response action using the first threat classification label and the second threat classification label.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- ENRICHED RULE-BASED THREAT DETECTION IN SECURITY SYSTEMS
- Publication number
- US20260320186A1
- Application number
- 19177477
- Filed
- Apr 11, 2025
- Published
- Oct 15, 2026
- Inventors
- 5
- Claims
- 20
Classified under
G06F 21/56 Physics & computingG06F 21/554 Physics & computingMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
- Microsoft patents security checks for AI chats using user and model profiles Oct 1, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.