Microsoft patents graph-based system to detect cloud security incidents
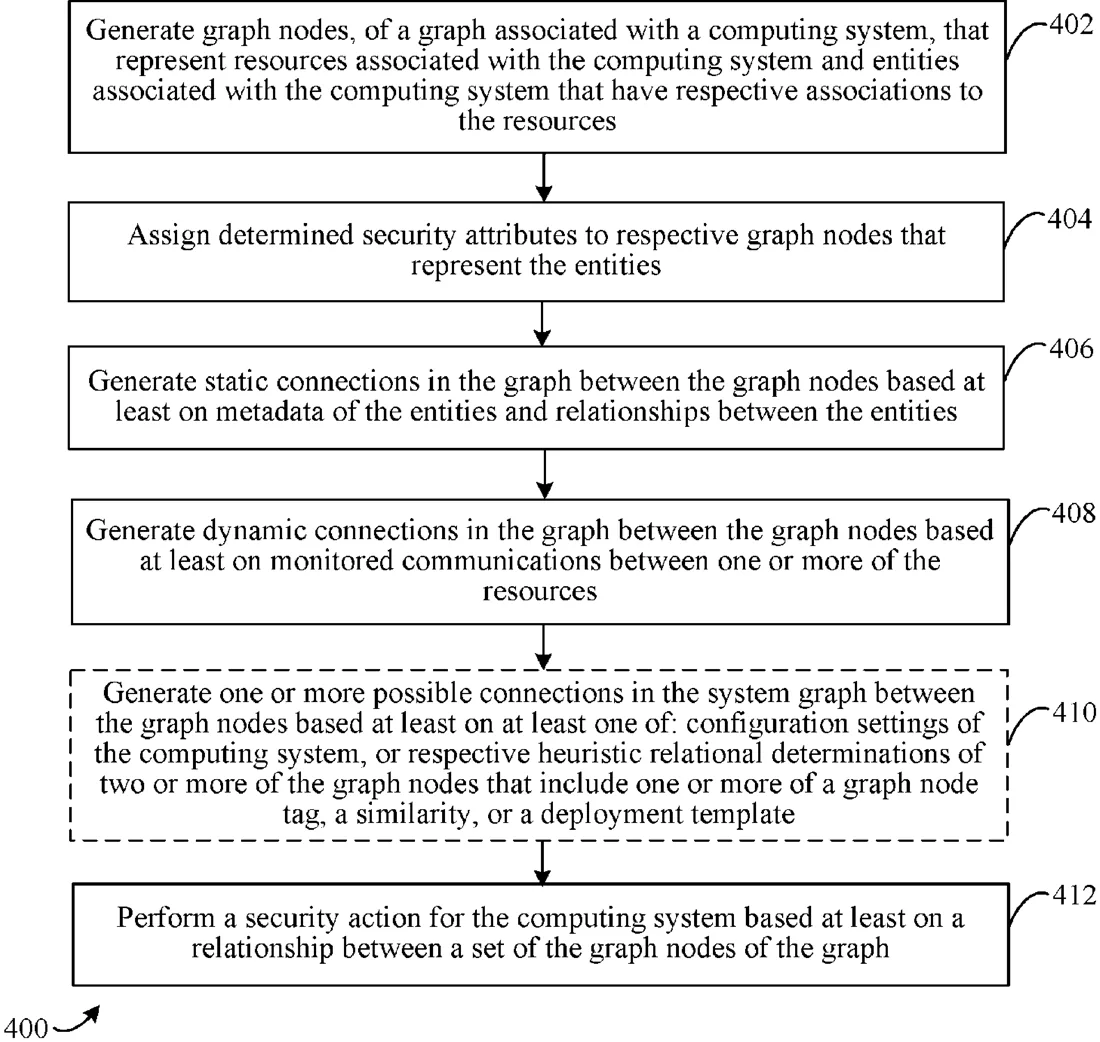
Microsoft describes a system that maps cloud resources and users into a visual graph to track how they connect. It uses this map to spot security threats and automatically apply safety rules.
In the filing’s own words
Context-aware security policies and incident identification, via automated cloud graph building with security overlays, are determined and performed by systems and platforms. Graph nodes, of a graph associated with a computing system, that represent resources associated with the computing system and entities associated with the computing system that have respective associations to the resources are generated. Security attributes are determined and assigned to the graph nodes that represent the entities and resources, and static and dynamic connections between the graph nodes are added to the graph. Additionally, possible connections in the graph between the graph nodes are added based on heuristic relational determinations of the graph nodes. From the graph, security incidents and kill chains are identified, context-aware security policies are generated and validated, and scopes and relationships of applications are identified. Accordingly, security actions are taken for the computing system.
What exactly they claim (claim 1)
1. A system, comprising: a processor; and a memory device that stores program code structured to cause the processor to: identify a security alert for at least one of a resource or an entity represented in a graph of a computing system, the graph including graph nodes representing resources and entities of the computing system, the entities having respective associations to the resources, the graph nodes representing the entities having assigned security attributes; identify a security incident based at least on the security alert and a relationship between a plurality of graph nodes of the graph; and perform a security action for the computer system based at least on the identified security incident.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- CONTEXT-AWARE SECURITY POLICIES AND INCIDENT IDENTIFICATION VIA AUTOMATED CLOUD GRAPH BUILDING WITH SECURITY OVERLAYS
- Publication number
- US20260303673A1
- Application number
- 19702698
- Filed
- Jun 9, 2026
- Published
- Oct 1, 2026
- Inventors
- 1
- Claims
- 20
Classified under
H04L 63/205 Electricity & electronicsMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
- Microsoft patents security checks for AI chats using user and model profiles Oct 1, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.