Microsoft patents AI that builds custom security shields for network attacks
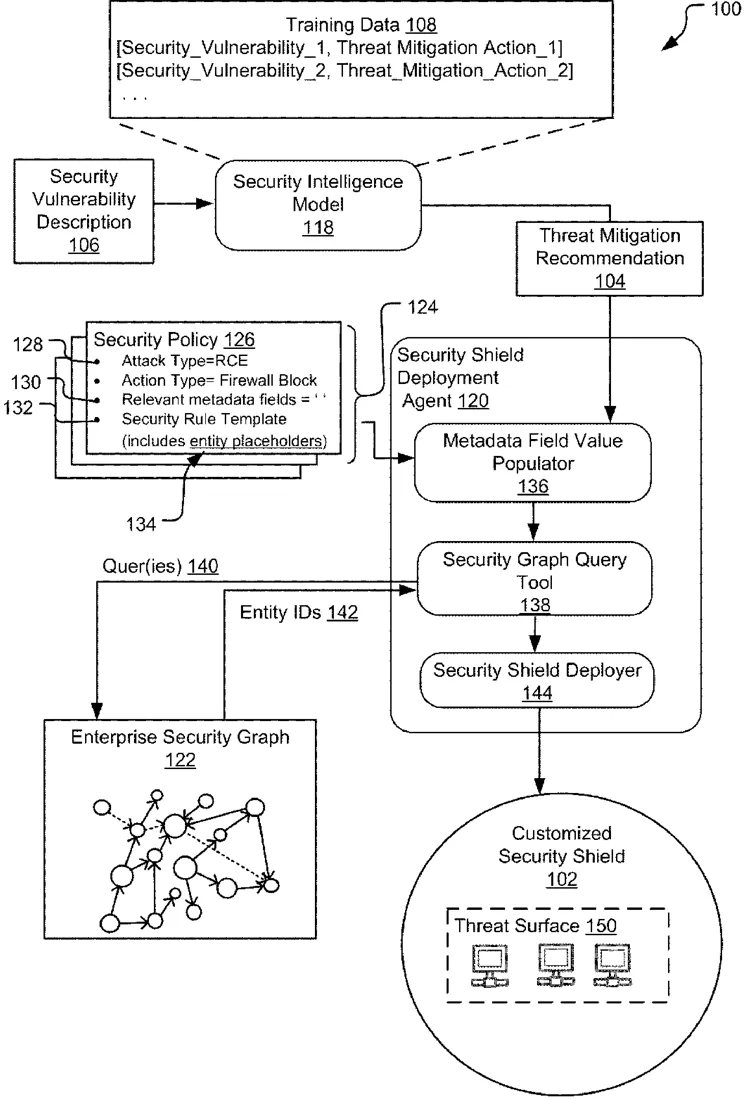
Microsoft describes a system that automatically creates and deploys specific security rules to protect network devices from known vulnerabilities. It works by reading a threat description, finding the affected devices in a company's security database, and filling in a rule template to block the attack.
In the filing’s own words
A method disclosed autonomously generates and deploys a customized security shield to protect specific network entities from an attack exploiting a security vulnerability. The method includes receiving description of a threat mitigation recommendation, identifying a security policy applicable to the threat mitigation recommendation, analyzing text of the threat mitigation recommendation to determine a value for at least one metadata field defined in the security policy, constructing a query to an enterprise security graph to identify entities stored in association with the value, populating a security rule template with entity identifiers obtained from the enterprise security graph in response to the query; and using the populated security rule template to deploy a customized security shield to protect the specific network entities from an attack exploiting the security vulnerability.
What exactly they claim (claim 1)
1. A system comprising: a security shield deployment agent stored in memory and executable by a processing system to: receive as input a description of a threat mitigation recommendation to address a security vulnerability; identify a security policy applicable to the threat mitigation recommendation, the security policy identifying a set of metadata fields and a security rule template containing placeholders for entities referenced in an enterprise security graph; analyze text of the threat mitigation recommendation to determine a value for at least one metadata field of the set of metadata fields defined in the security policy; construct a query to the enterprise security graph to determine an entity identifier corresponding to an entity or resource of a specific network, the entity identifier stored in the enterprise security graph in association with the value for the at least one metadata field; populate the security rule template with the entity identifier obtained from the enterprise security graph in response to the query; and based at least in part on population of the security rule template, deploy a customized security shield to protect a network device or resource identified by the entity identifier from an attack exploiting the security vulnerability.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- ARTIFICIAL INTELLIGENCE FOR CUSTOMIZED SECURITY SHIELD DEPLOYMENT
- Publication number
- US20260300478A1
- Application number
- 19094231
- Filed
- Mar 28, 2025
- Published
- Oct 1, 2026
- Inventors
- 2
- Claims
- 20
Classified under
G06F 21/554 Physics & computingG06F 2221/034 Physics & computingMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
- Microsoft patents security checks for AI chats using user and model profiles Oct 1, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.