Microsoft patents system that adapts DDoS protection to server load
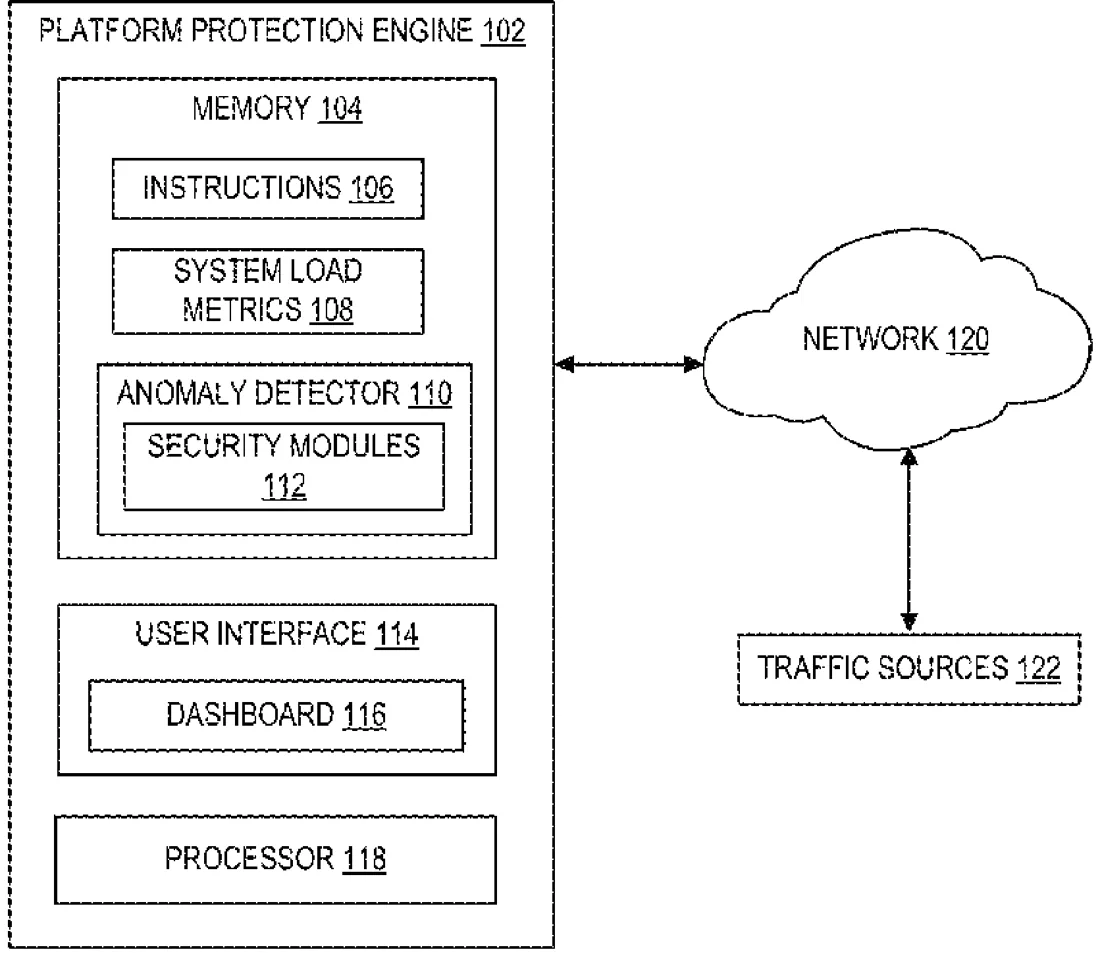
This patent describes a security system that monitors a computer's workload to detect and block cyberattacks. It uses a set of security checks that adjust their importance based on which system resources are currently under stress, allowing the system to pinpoint and block the specific source of an attack while letting normal traffic continue.
In the filing’s own words
Adaptive multi-dimensional anomaly detection is provided. System load metrics of a computing device are monitored. Multi-dimensional analysis of traffic data from a plurality of traffic sources is performed with security modules of an anomaly detector on the computing device. A traffic source is identified from the plurality of traffic sources based on the multi-dimensional analysis of traffic data from the plurality of traffic sources and associated historical traffic data. An action is performed on the traffic data from the identified traffic source, while the traffic data from the plurality of traffic sources other than the identified traffic source is allowed unaffected.
What exactly they claim (claim 1)
1. A system for distributed denial-of-service (DDoS) protection, the system comprising: a processor; and a memory storing instructions that upon execution by the processor perform operations comprising: monitoring system load metrics of a computing device; using the system load metrics, performing multi-dimensional analysis of traffic data from a plurality of traffic sources with security modules of an anomaly detector on the computing device, wherein performing the multi-dimensional analysis comprises generating an aggregate anomaly score from the security modules using adaptive weighting based on the system load metrics to dynamically adjust influence of individual anomaly scores from the security modules, wherein the adaptive weighting increases a weight applied to a first anomaly score from a first security module relative to weights applied to anomaly scores from remaining security modules based on a system load metric indicating exhaustion of a resource type associated with the first security module; identifying a traffic source from the plurality of traffic sources that contributes most to the aggregate anomaly score based on the multi-dimensional analysis of traffic data from the plurality of traffic sources and associated historical traffic data of the plurality of traffic sources; and blocking the traffic data from the identified traffic source and allowing the traffic data from the plurality of traffic sources other than the identified traffic source.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- Adaptive multi-dimensional anomaly detection
- Patent number
- US12771713B2
- Application number
- 18657731
- Filed
- May 7, 2024
- Granted
- Oct 20, 2026
- Inventors
- 3
- Claims
- 20
Classified under
H04L 63/1458 Electricity & electronicsH04L 43/062 Electricity & electronicsH04L 43/0882 Electricity & electronicsH04L 63/1425 Electricity & electronicsMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
- Microsoft patents security checks for AI chats using user and model profiles Oct 1, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.