Microsoft patents security check using device history logs
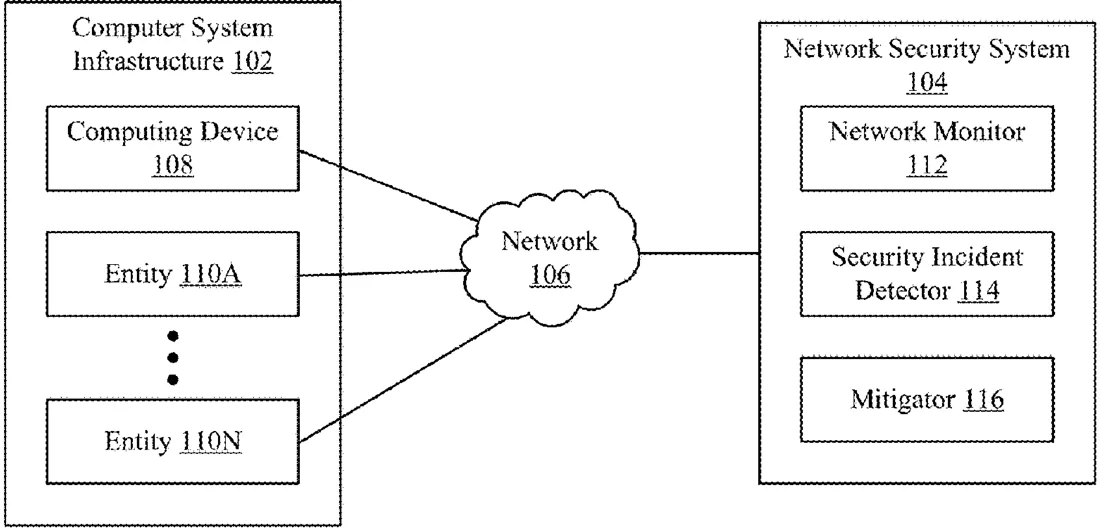
Microsoft has been granted a patent for a method that detects security breaches by tracking how a computer's settings change over time. The system compares current configuration logs against historical records using hash values to spot unauthorized changes. If the data suggests a security incident, the system automatically generates an alert.
In the filing’s own words
Security incident detection based on historian configuration data collected over time is described. Historic configuration data associated with a computing device is updated based on received configuration data indicative of a change in configuration of the computing device in a computer system. The historic configuration data indicates changes to configurations of the computing device over a time period. A determination that relationship between the computing device and an entity of the computer system has changed is made based on the updated historic configuration data. The updated historic configuration data is provided as input to a machine learning (ML) model configured to generate an indication of whether the updated historic configuration data evidences a security incident. In response to the ML model generating an indication that the updated historic configuration data evidences a security incident, a security alert indicative of the evidenced security incident is generated.
What exactly they claim (claim 1)
1. A method comprising: generating a first hash value based on an event record associated with a computing device of a computer system; storing the first hash value in a hash store; receiving, from a historian data store, a configuration log associated with the computing device; generating a second hash value based on the configuration log associated with the computing device; determining, based on a comparison between the first hash value and the second hash value, a security incident with respect to the computing device; and generating a security alert indicative of the security incident with respect to the computing device.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- Security incident detection based on historian configuration data collected over time
- Patent number
- US12764149B2
- Application number
- 18901879
- Filed
- Sep 30, 2024
- Granted
- Oct 13, 2026
- Inventors
- 3
- Claims
- 20
Classified under
H04L 63/1425 Electricity & electronicsMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
- Microsoft patents security checks for AI chats using user and model profiles Oct 1, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.