Microsoft patents system to flag suspicious cloud admin actions
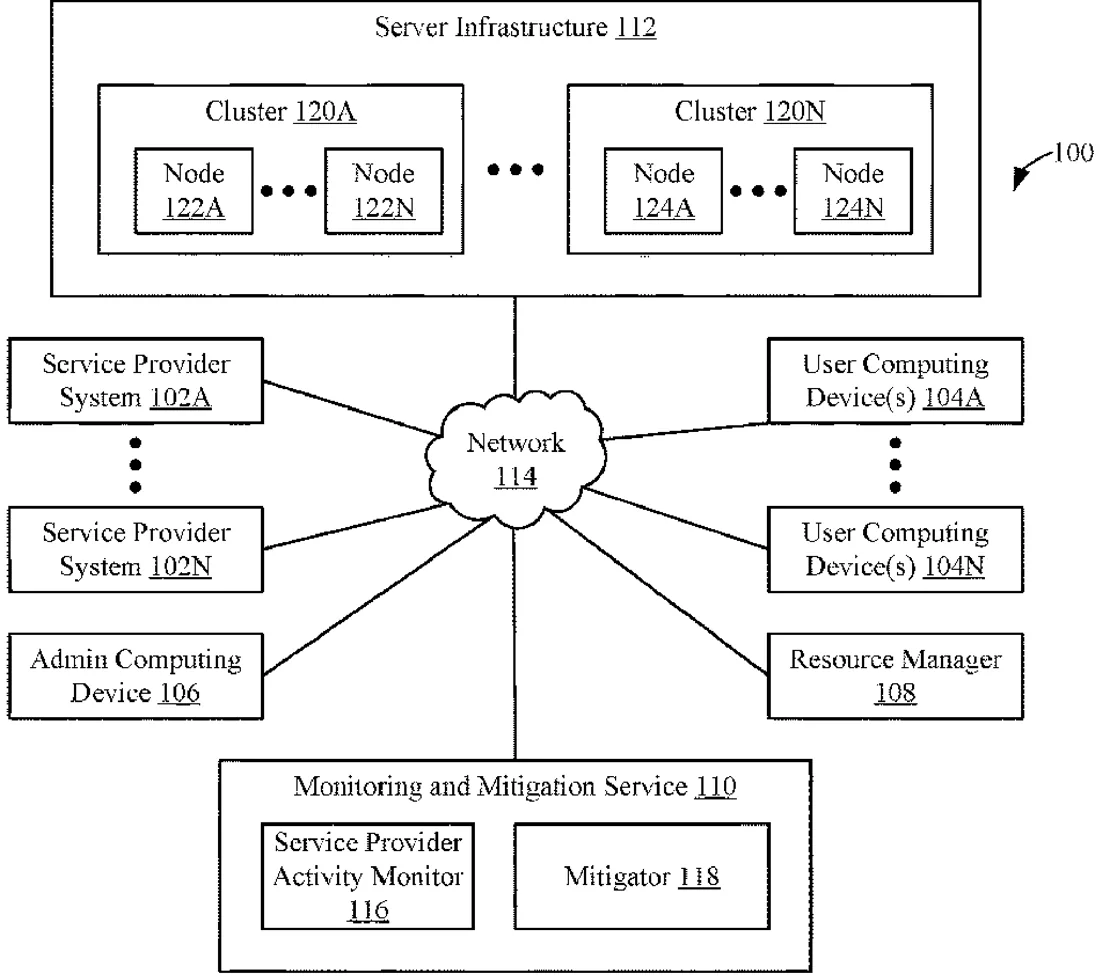
Microsoft has patented a method for detecting suspicious behavior in cloud environments by analyzing logs of administrative actions. The system compares current operations against the historical patterns of the service provider to calculate a risk score. If the activity looks unusual, the system automatically generates a security alert.
In the filing’s own words
Malicious service provider activity detection is enabled. A first log is obtained. The first log comprises a record of a first control plane operation executed on behalf of a first entity. A service provider associated with the execution of the first control plane operation is identified. The service provider has privileges to execute control plane operations on behalf of the first entity. A first malicious activity score is determined based at least on the service provider. The first malicious activity score is indicative of a degree to which the first control plane operation is anomalous with respect to the first entity. A determination that the first control plane operation potentially corresponds to malicious activity is made based at least on the determined first malicious activity score. Responsive to determining that the first control plane operation potentially corresponds to malicious activity, a security alert is generated.
What exactly they claim (claim 1)
1. A method comprising: obtaining a first log that comprises a record of a first control plane operation executed on behalf of a first entity; identifying a service provider associated with the execution of the first control plane operation, the service provider having privileges to execute control plane operations on behalf of the first entity; determining, based at least on a comparison of the execution of the first control plane operation and historic activity of the service provider, a first malicious activity score indicative of a degree to which the first control plane operation is anomalous with respect to the first entity; determining, based at least on the determined first malicious activity score, the first control plane operation potentially corresponds to malicious activity; and responsive to determining that the first control plane operation potentially corresponds to malicious activity, generating a security alert.
Facts
- Company
- Microsoft (Microsoft Technology Licensing, LLC)
- Official title
- Malicious service provider activity detection
- Patent number
- US12764140B2
- Application number
- 18313592
- Filed
- May 8, 2023
- Granted
- Oct 13, 2026
- Inventors
- 3
- Claims
- 20
Classified under
H04L 63/1425 Electricity & electronicsH04L 63/1441 Electricity & electronicsMore from Microsoft in Security & privacy
- Microsoft patents system to call 911 for others during video calls Sep 22, 2026
- Microsoft patents system to block fake code suggested by AI Sep 15, 2026
- Microsoft patents one-way data flow to block network attacks Sep 10, 2026
- Microsoft patents voice coding that hides speaker identity for secure calls Sep 17, 2026
- Microsoft patents security checks for AI chats using user and model profiles Oct 1, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.