Google patents security system that maps company data to spot threats
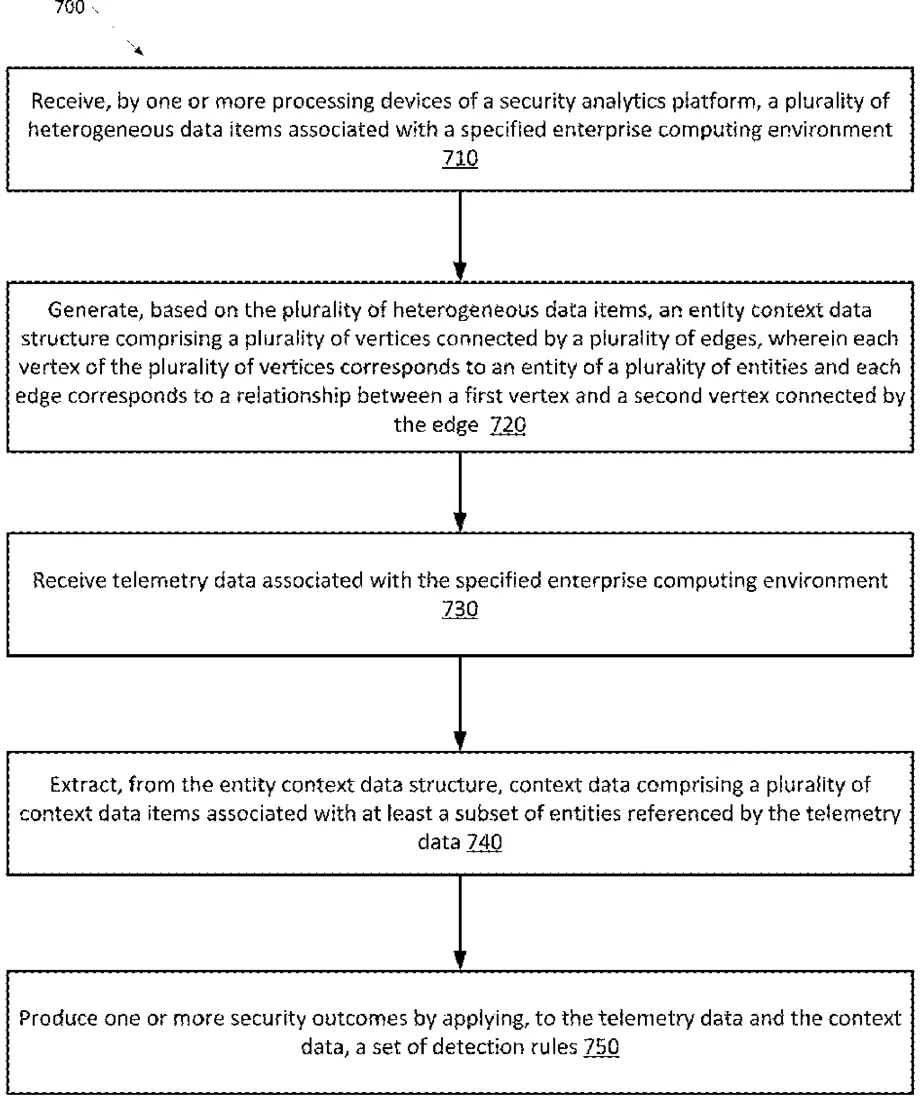
This patent describes a method for detecting security threats in a company's computer network. It works by building a map of how different digital assets and users are connected, then checking live activity data against this map to find suspicious behavior.
In the filing’s own words
Aspects of the disclosure are directed to entity context-based security threat detection by a security analytics platform. A plurality of heterogeneous data items associated with a specified enterprise computing environment can be received by one or more processing devices of a security analytics platform. An entity context data structure comprising a plurality of vertices connected by a plurality of edges can be generated based on the plurality of heterogeneous data items. Telemetry data associated with the specified enterprise computing environment can be received. Context data comprising a plurality of context data items associated with at least a subset of entities referenced by the telemetry data can be extracted from the entity context data structure. One or more security outcomes can be produced by applying a set of detection rules to the telemetry data and the context data.
What exactly they claim (claim 1)
1. A method, comprising: receiving, by one or more processing devices of a security analytics platform, a plurality of heterogeneous data items associated with a specified enterprise computing environment; cross-validating a first subset of the plurality of heterogeneous data items and a second subset of the plurality of heterogeneous data items; generating, based on the plurality of heterogeneous data items, an entity context data structure comprising a plurality of vertices connected by a plurality of edges, wherein each vertex of the plurality of vertices corresponds to an entity of a plurality of entities and each edge corresponds to a relationship between a first vertex and a second vertex connected by the edge; receiving telemetry data associated with the specified enterprise computing environment; extracting, from the entity context data structure, context data comprising a plurality of context data items associated with at least a subset of the entities referenced by the telemetry data; and producing one or more security outcomes by applying, to the telemetry data and the context data, a set of detection rules.
Facts
- Company
- Google (Google LLC)
- Official title
- Entity context-based security threat detection by a security analytics platform
- Patent number
- US12756723B2
- Application number
- 19054284
- Filed
- Feb 14, 2025
- Granted
- Oct 6, 2026
- Inventors
- 5
- Claims
- 17
Classified under
H04L 63/1416 Electricity & electronicsG06F 16/215 Physics & computingMore from Google in Security & privacy
- Google patents privacy score for third-party apps Sep 22, 2026
- Google patents phone feature to disable unknown trackers Oct 8, 2026
- Google patents local face recognition for smart home cameras Sep 10, 2026
- Google patents system that finds and fills in email verification codes Sep 17, 2026
- Google patents AI agents that automatically investigate network security threats Oct 8, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.