Nvidia patents secure way for virtual apps to use encryption keys
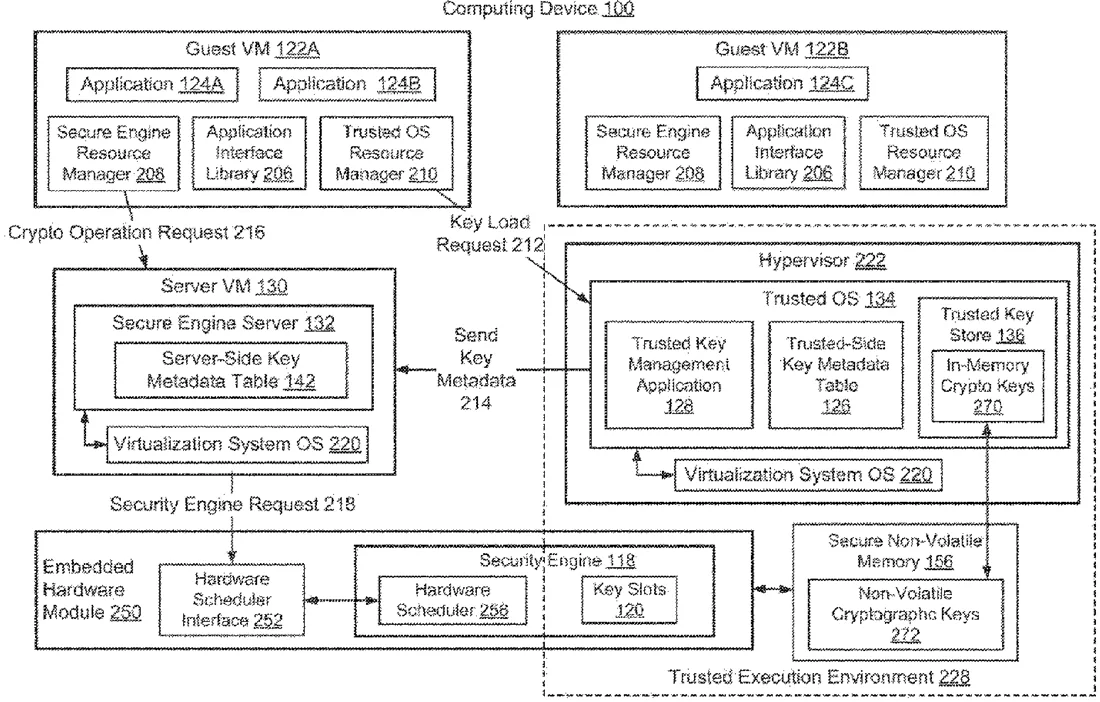
Nvidia describes a method where an application running in a virtual machine asks a secure hardware area to perform encryption tasks. The system uses a temporary ID to find the right key in a protected slot, performs the math, and sends the result back to the app.
In the filing’s own words
In various examples, the disclosed techniques include receiving, from an application executing in a virtual machine (VM), a request to perform a cryptographic operation, wherein the request specifies an ephemeral key identifier and source data. The techniques also determine, using key metadata received from a trusted execution environment, a key slot identifier associated with the ephemeral key identifier, wherein the key slot identifier identifies a key slot in which a cryptographic key is stored. The techniques further cause the cryptographic operation to be performed on the source data in the trusted execution environment using the cryptographic key, where the cryptographic key used to perform the cryptographic operation is accessed from the key slot identified by the key slot identifier. The techniques further provide, to the application, a cryptographic operation result received form the trusted execution environment.
What exactly they claim (claim 1)
1. A method, comprising: receiving, from an application executing in a virtual machine (VM), a request to perform a cryptographic operation, wherein the request specifies an ephemeral key identifier and source data; determining, using key metadata received from a trusted execution environment, a key slot identifier associated with the ephemeral key identifier, wherein the key slot identifier identifies a key slot in which a cryptographic key is stored; causing the cryptographic operation to be performed on the source data in the trusted execution environment using the cryptographic key, wherein the cryptographic key used to perform the cryptographic operation is accessed from the key slot identified by the key slot identifier; and providing, to the application, a cryptographic operation result received from the trusted execution environment.
Facts
- Company
- Nvidia (NVIDIA CORPORATION)
- Official title
- Secure virtualized cryptographic subsystems for autonomous systems and applications
- Patent number
- US12754756B2
- Application number
- 18569584
- Filed
- Oct 11, 2023
- Granted
- Oct 6, 2026
- Inventors
- 9
- Claims
- 20
Classified under
G06F 9/45558 Physics & computingH04L 9/0897 Electricity & electronicsG06F 2009/45587 Physics & computingMore from Nvidia in Security & privacy
- Nvidia patents AI tool that finds security flaws in system diagrams Oct 22, 2026
- Nvidia patents chip protection against clock speed attacks Sep 22, 2026
- Nvidia patents hardware method to keep encryption keys hidden from software Oct 13, 2026
- Nvidia patents system that checks secret passwords against rules Sep 3, 2026
- Nvidia patents database search that hides restricted data in real time Sep 17, 2026
Summaries are simplified from the filing’s own abstract and first claim. A patent filing is not a product announcement.
Patent data and drawings: U.S. Patent and Trademark Office (USPTO). Nebula is not affiliated with or endorsed by the USPTO.